Android - App Fingerprint - Monitor (Pro)
The app signature shows who signed the app. If someone else rebuilds your game, the signature changes. You can check that locally. You do not need a server.
Walkthrough: Protecting an Android build.
Monitor
AndroidPackageFingerprintMonitor (namespace GUPS.AntiCheat.Monitor.Android) reads the app signature. The raw signature is binary, so the monitor turns it into readable text with a hash method you choose. It then sends an AndroidFingerprintStatus.
Status
The monitor sends an AndroidFingerprintStatus:
public struct AndroidFingerprintStatus : IAndroidStatus
{
    // True if the fingerprint could not be retrieved (e.g. a JNI failure).
    public bool FailedToRetrieveData { get; }

    // The algorithm used to compute the fingerprint.
    public string Algorithm { get; }

    // The hex-encoded signing certificate fingerprint of the running app.
    public string Fingerprint { get; }
}
- FailedToRetrieveData: The signature could not be read. The other values are not valid.
- Algorithm: Which hash method was used. See the table below.
- Fingerprint: The signature text of the running app.
Lifecycle and timing
The monitor reads the signature once, when it starts. It then sends one AndroidFingerprintStatus. If the read fails, it still sends a status, with FailedToRetrieveData set to true.
Configuration
The hash method and the expected signature are set in Project Settings, not on the component. See Hash algorithm below.
Development builds
Verify development builds is off by default. While it is off, the check skips development builds and the Editor. Turn it on while you test.
Turn on Verify development builds to also check development builds and the Editor.
Supported platforms
Android only.
Requirements
Android 4.4 (API level 19) or newer.
How to use
Add AndroidPackageFingerprintMonitor as a child of the AntiCheat-Monitor. Choose the hash method in Project Settings. Pair the monitor with AndroidPackageTamperingDetector.
Add the component
Add AndroidPackageFingerprintMonitor from GUPS.AntiCheat.Monitor.Android. A child of the monitor is the best place.
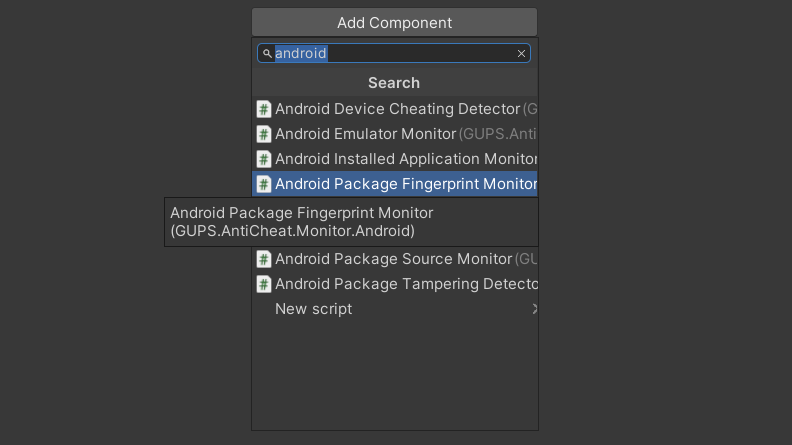
Add the AndroidPackageFingerprintMonitor component.
Hash algorithm
AntiCheat can use these methods:
| Method | Notes |
|---|---|
| None | No hash is calculated |
| MD5 | Not recommended |
| SHA1 | Not recommended |
| SHA256 | Recommended |
| SHA384 | Stronger than SHA-256 |
| SHA512 | Stronger than SHA-256 |
Open Edit > Project Settings > GuardingPearSoftware > AntiCheat. Go to Android - App Fingerprint - Settings. Turn on Verify app fingerprint and pick a method. SHA-256 is the recommended choice.
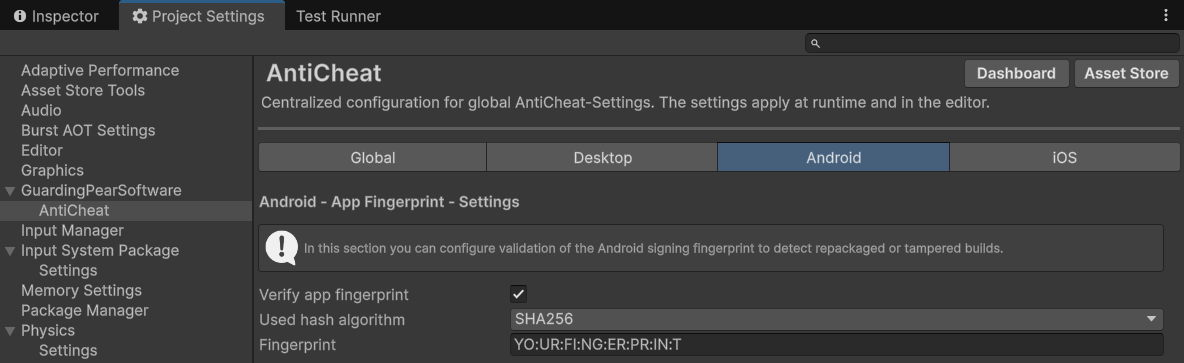
Fingerprint settings.
Read the status in code
You can also listen yourself. Subscribe returns an IDisposable. Dispose it when you want to stop.
using System;
using GUPS.AntiCheat.Core.Watch;
using GUPS.AntiCheat.Monitor.Android;
using UnityEngine;

public class AndroidFingerprintStatusLogger : MonoBehaviour, IObserver<IWatchedSubject>
{
    private void Start()
    {
        var monitor = GetComponentInChildren<AndroidPackageFingerprintMonitor>();
        monitor.Subscribe(this);
    }

    public void OnNext(IWatchedSubject subject)
    {
        if (subject is AndroidFingerprintStatus status)
        {
            if (status.FailedToRetrieveData)
            {
                Debug.LogWarning("Could not read the app fingerprint.");
                return;
            }

            Debug.Log($"Fingerprint ({status.Algorithm}): {status.Fingerprint}");
        }
    }

    public void OnError(Exception error) { }
    public void OnCompleted() { }
}
Detect the wrong signature
To compare the signature with yours, use the Android package tampering detector.